Coinbase CEO details North Korean hiring infiltration and $20m bounty
Brian Armstrong said applicants used off-camera coaching during interviews, while attackers offered staff hundreds of thousands of dollars to photograph internal screens.
Key takeaways
- 1Coinbase CEO Brian Armstrong said applicants for remote roles received off-camera coaching during live video interviews.
- 2Attackers offered support staff hundreds of thousands of dollars to smuggle phones into offices and photograph screens.
- 3Coinbase set up a $20 million reward for information leading to the arrest or conviction of those responsible.
- 4The exchange introduced mandatory in-person US orientation and restricted system access for support personnel.
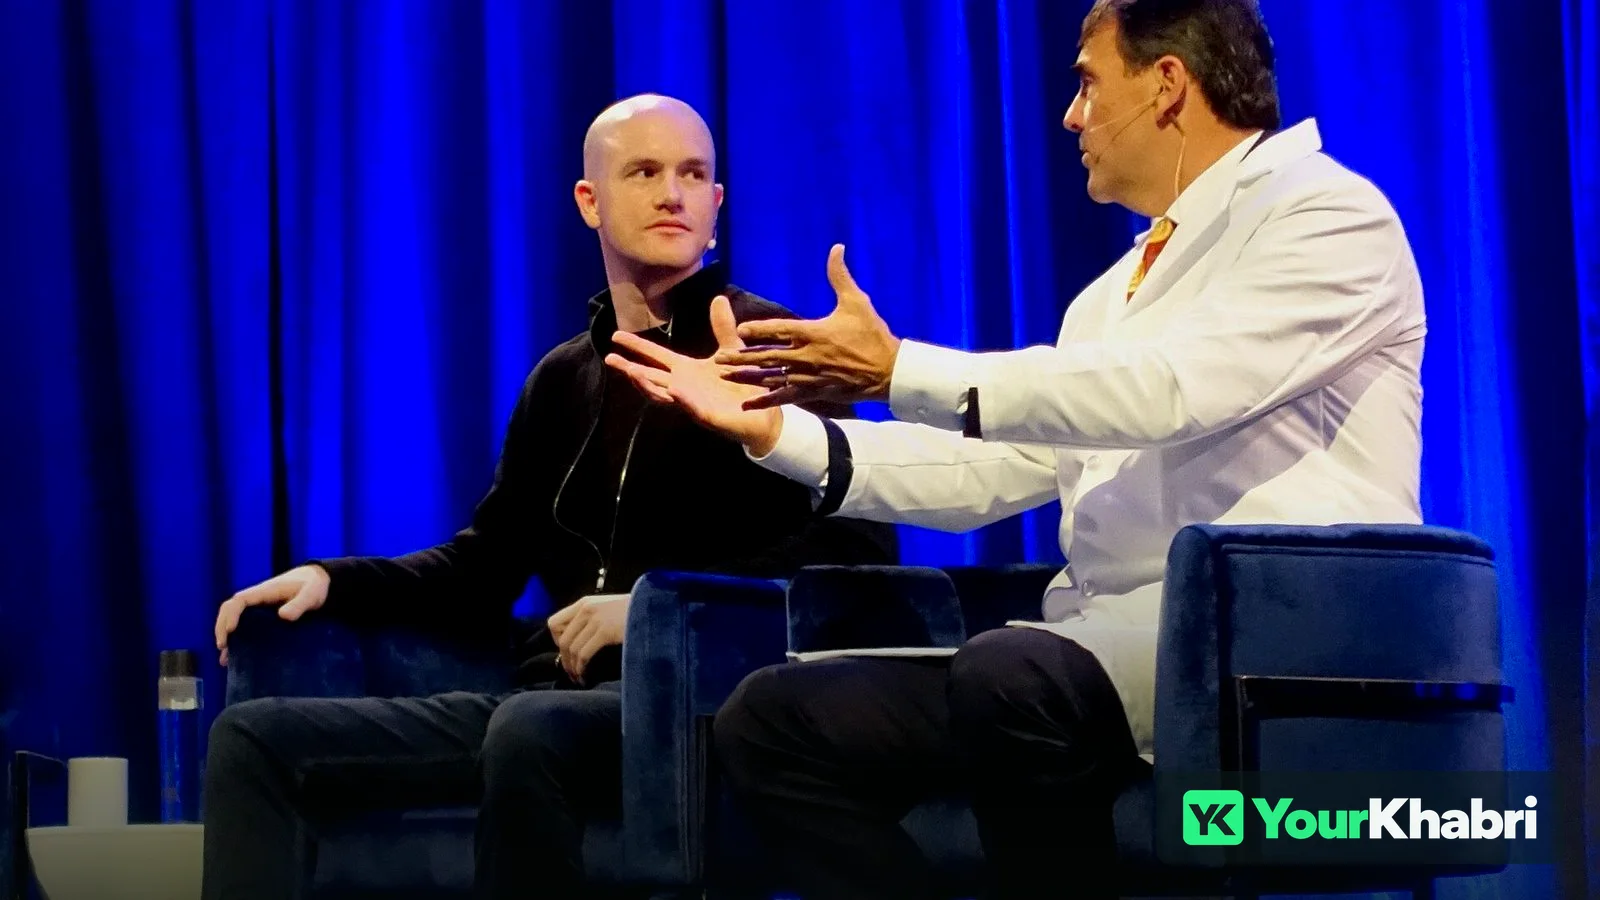
Coinbase co-founder and Chief Executive Officer Brian Armstrong said North Korean hackers targeted the cryptocurrency exchange by applying for remote jobs and offering support staff hundreds of thousands of dollars to photograph internal screens. Speaking in an interview with Stripe, Armstrong said operatives attempted to gain access to internal systems, prompting the exchange to set up a $20 million bounty for information leading to their arrest or conviction.
During video job interviews for remote positions, several applicants received off-camera coaching from accomplices in real time, Armstrong said. In response to the hiring attempts, Coinbase made in-person orientation in the United States mandatory for new hires and introduced stricter identity verification checks for employees accessing sensitive systems.
Beyond fake job applications, attackers attempted to recruit existing employees directly. Armstrong said attackers offered support workers hundreds of thousands of dollars to smuggle mobile phones into operational areas and photograph administrative screens. Coinbase responded by restricting system access rights across its customer support teams.
The tactics focus on human access points rather than technical vulnerabilities. State-backed groups targeting digital asset firms frequently seek entry through remote contractors and customer service personnel to bypass perimeter security controls.
Coinbase has maintained updated internal security rules following the incidents, including restricted data access for support staff and compulsory physical verification for staff based in the United States. The exchange did not report any compromise of customer funds linked to the recruitment or bribery attempts.
Reported and edited by the YourKhabri desk under our editorial policy. Nothing here is investment advice.