Blockstream launches institutional Bitcoin custody system with Thales
The platform integrates hardware security modules with multi-Party Computation to execute key signing fully inside dedicated offline hardware.
Key takeaways
- 1Blockstream and Thales launched a joint institutional custody system on 13 November 2026.
- 2The system executes the entire multi‑party computation signing process inside hardware security modules.
- 3Adam Back cited Binance's $6.3bn breach to highlight risks in connected signing infrastructure.
- 4Back warned that AI tools will help attackers spot implementation flaws in complex custody software.
Blockstream launched an institutional digital asset custody solution developed in partnership with French technology group Thales on 13 November 2026. The platform integrates hardware security modules from Thales with Blockstream's Secure Multi-Party Computation technology, enabling institutional investors to authorise Bitcoin transfers without exposing cryptographic keys to external networks.
Traditional multi-party computation protocols distribute cryptographic signing tasks across multiple connected devices, which frequently perform portions of the key calculation in software environments outside dedicated hardware. Blockstream said the architecture runs the entire multi-party signing process directly within the physical boundary of Thales hardware security modules, preventing transaction authorisation data from traversing unsecure memory or external servers.
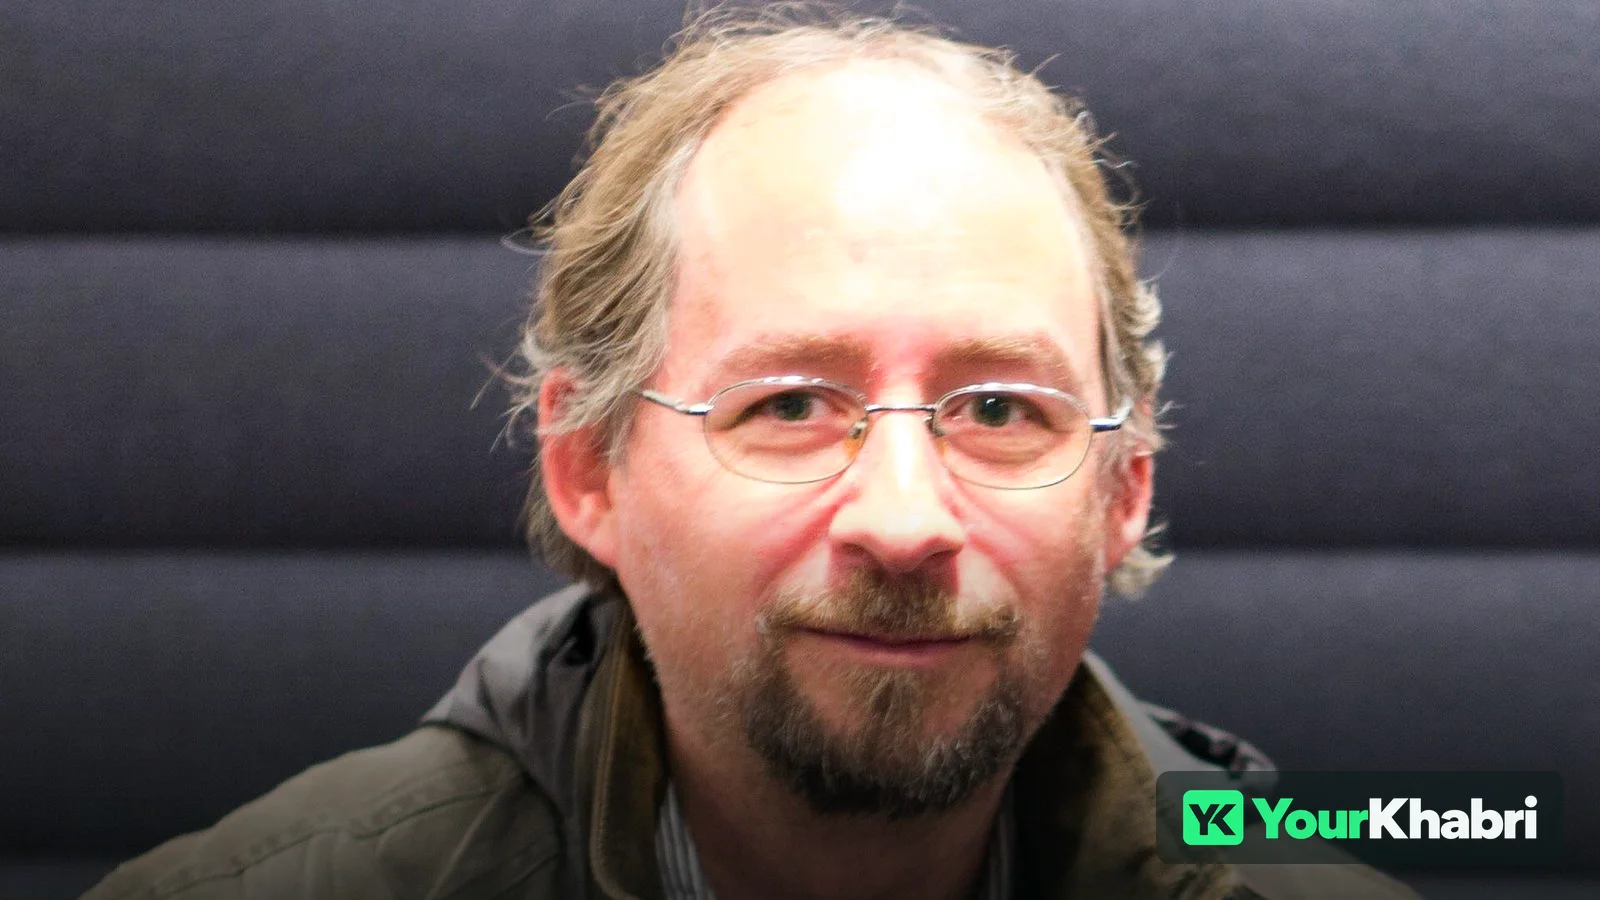
Blockstream co-founder and chief executive Adam Back, the cryptographer whose Hashcash proof-of-work algorithm laid the technical foundation for Bitcoin, said conventional multi-party computation designs carry structural flaws for institutional custody. He said typical protocols are highly interactive and demand frequent communication between devices, making them incompatible with fully air‑gapped cold storage operations.
Back pointed to a $6.3bn cyberattack against Binance as an example of the risks associated with online wallet‑signing infrastructure. Internal investigations into that attack revealed that intruders breached employee devices to capture administrative credentials, which then allowed unauthorized access to the exchange's signing key infrastructure.
Back warned that the spread of artificial intelligence models will compound existing security challenges across the digital asset industry. He said artificial intelligence applications can assist malicious actors in identifying minute coding errors and protocol flaws that human auditors overlook. Back urged institutional custodians to reduce their attack surface by moving assets into simple offline cold storage systems.
Reported and edited by the YourKhabri desk under our editorial policy. Nothing here is investment advice.